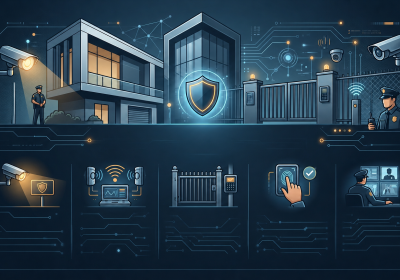
When business owners think about security, the conversation tends to split into two separate boxes: “cybersecurity” and “everything else.” That split is understandable, but it’s also outdated. A modern business isn’t protected by a single system — it’s protected by how well several layers work together: physical premises, digital systems, financial controls, and the people who run all three.
A company that spends heavily on one layer while ignoring the others isn’t secure. It just has one very well-defended door in a house with the windows left open.
Why Business Security Is Different From Personal Security
A home has one household to protect. A business has employees, customers, vendors, contractors, and sometimes the public moving through its space and systems every day. That complexity is exactly why business security requires more structure — informal habits that work fine at home don’t scale once dozens or hundreds of people are involved.
The stakes are also different. A security failure at home is usually personal. A security failure at a business can mean lost revenue, legal liability, damaged customer trust, regulatory penalties, or in serious cases, the survival of the company itself.
The Core Areas of Business Security
1. Physical premises This includes building access, visitor management, secure storage for equipment and inventory, and surveillance of entry points and high-value areas. Even service-based or remote-first businesses usually have something physical worth protecting — laptops, servers, files, or office equipment.
2. Information and data security Customer data, financial records, intellectual property, and internal communications all need protection from both external attackers and internal mishandling. This covers everything from password policies to how sensitive files are stored, shared, and disposed of.
3. Financial controls Fraud — both external and internal — is one of the most underestimated risks a business faces. Clear approval processes for payments, separation of financial duties, and regular audits reduce opportunities for both deliberate fraud and honest mistakes that compound into bigger problems.
4. Employee and access management Not everyone in a business needs access to everything. Role-based access, structured onboarding and offboarding, and clear policies around shared credentials all reduce the number of ways things can go wrong.
5. Vendor and third-party risk Every vendor, contractor, or partner with access to your systems, facility, or data is effectively an extension of your security posture. A weak link in a vendor’s practices can become a weak link in yours.
Where Businesses Commonly Get Exposed
- Access that outlives its purpose. Former employees or contractors retaining building access, system logins, or shared passwords long after their engagement ends.
- Undocumented processes. When only one person knows how something works — a critical login, a vendor relationship, a financial process — the business is exposed if that person is unavailable or leaves.
- Inconsistent enforcement. Security policies that exist on paper but aren’t actually followed day to day tend to fail exactly when they’re needed most.
- Underestimating internal risk. Most security conversations focus on outside threats, but a meaningful share of incidents involve employees, whether through negligence, error, or intentional misuse.
- Treating security as a one-time project. A system set up correctly two years ago can quietly become outdated as the business grows, adds tools, or changes how it operates.
Building a Practical Business Security Approach
Security doesn’t need to be built all at once, and it doesn’t need an enterprise budget to be meaningful. A reasonable approach:
- Identify what actually needs protecting. Data, equipment, cash flow, reputation — priorities differ by business type.
- Map who has access to what, and whether that access still makes sense.
- Formalize the basics — onboarding/offboarding checklists, approval chains for payments, visitor policies, and data handling rules.
- Train employees regularly, not just once. Most security failures involve people, not technology, so ongoing awareness matters more than a single onboarding session.
- Review and adjust periodically. New hires, new tools, new locations, and business growth all change the risk picture.
- Plan for when something goes wrong, not just how to prevent it. A clear incident response plan — who’s notified, what steps are taken, how it’s documented — limits damage when prevention isn’t enough.
The Bottom Line
Business security works best when it’s treated as a shared responsibility across the organization, not a single department’s job or a checklist completed once and forgotten. The businesses that handle it well don’t necessarily spend the most — they build consistent habits, keep access and processes current, and treat physical, digital, and financial protection as parts of the same system rather than separate concerns.
Ultimately, business security isn’t about eliminating every risk. It’s about making sure that when something does go wrong, it’s a manageable setback rather than an existential one.